
Organization
Manage organization members, projects, and settingsEdit
Manage your organization's projects, members, CLI tokens, AI SRE setup, and audit trails from the Organization page in the sidebar.
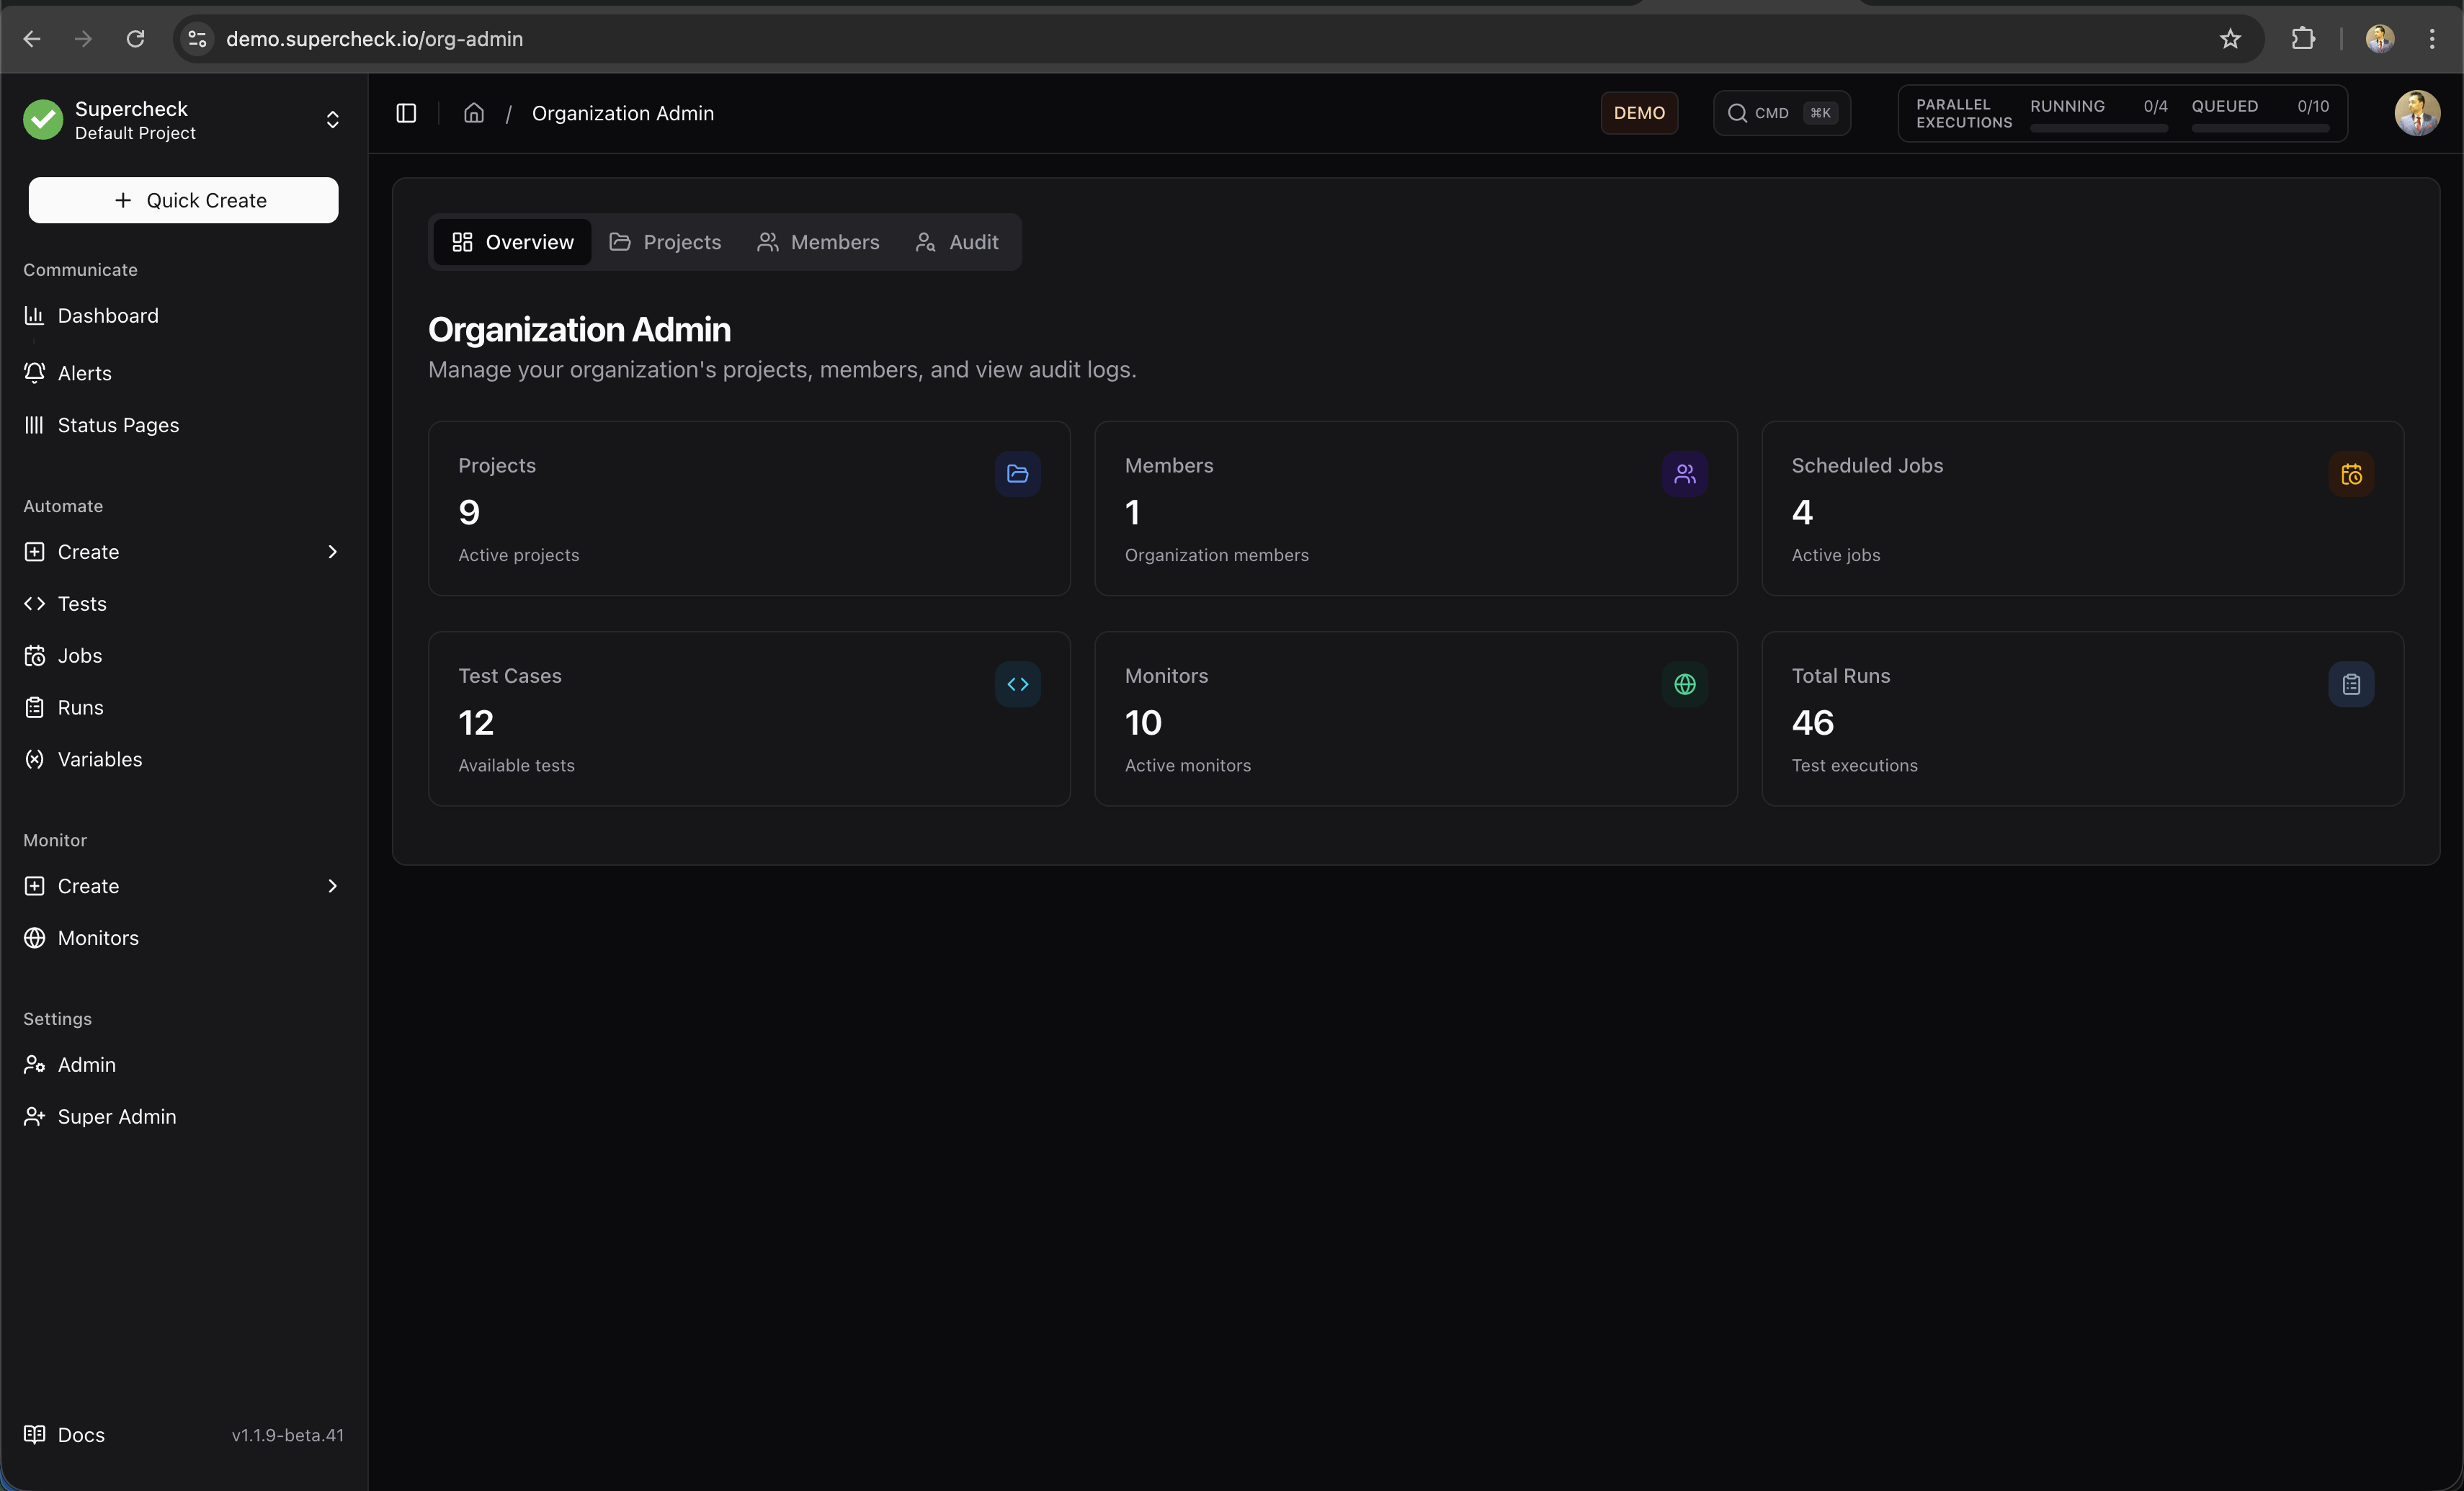
Your default organization
Signup assigns one default organization and a default project. There is no organization creation or switching menu. Create and switch projects using the project selector and Admin → Projects.
You can accept invitations to projects in other organizations while keeping your default organization. Those projects appear in the project selector with their team name. All active projects in a joined team are visible and selectable with read-only access. Project editor and project admin assignments grant additional permissions only in the selected projects; they do not hide other team projects. Owning your default organization does not grant administrative access to another team.
New users signing up through an invitation join the inviting team without creating a separate organization. Use the project selector to choose the team and project you need.
Projects
Organization administrators can create and manage projects. Project admins can update their assigned projects.
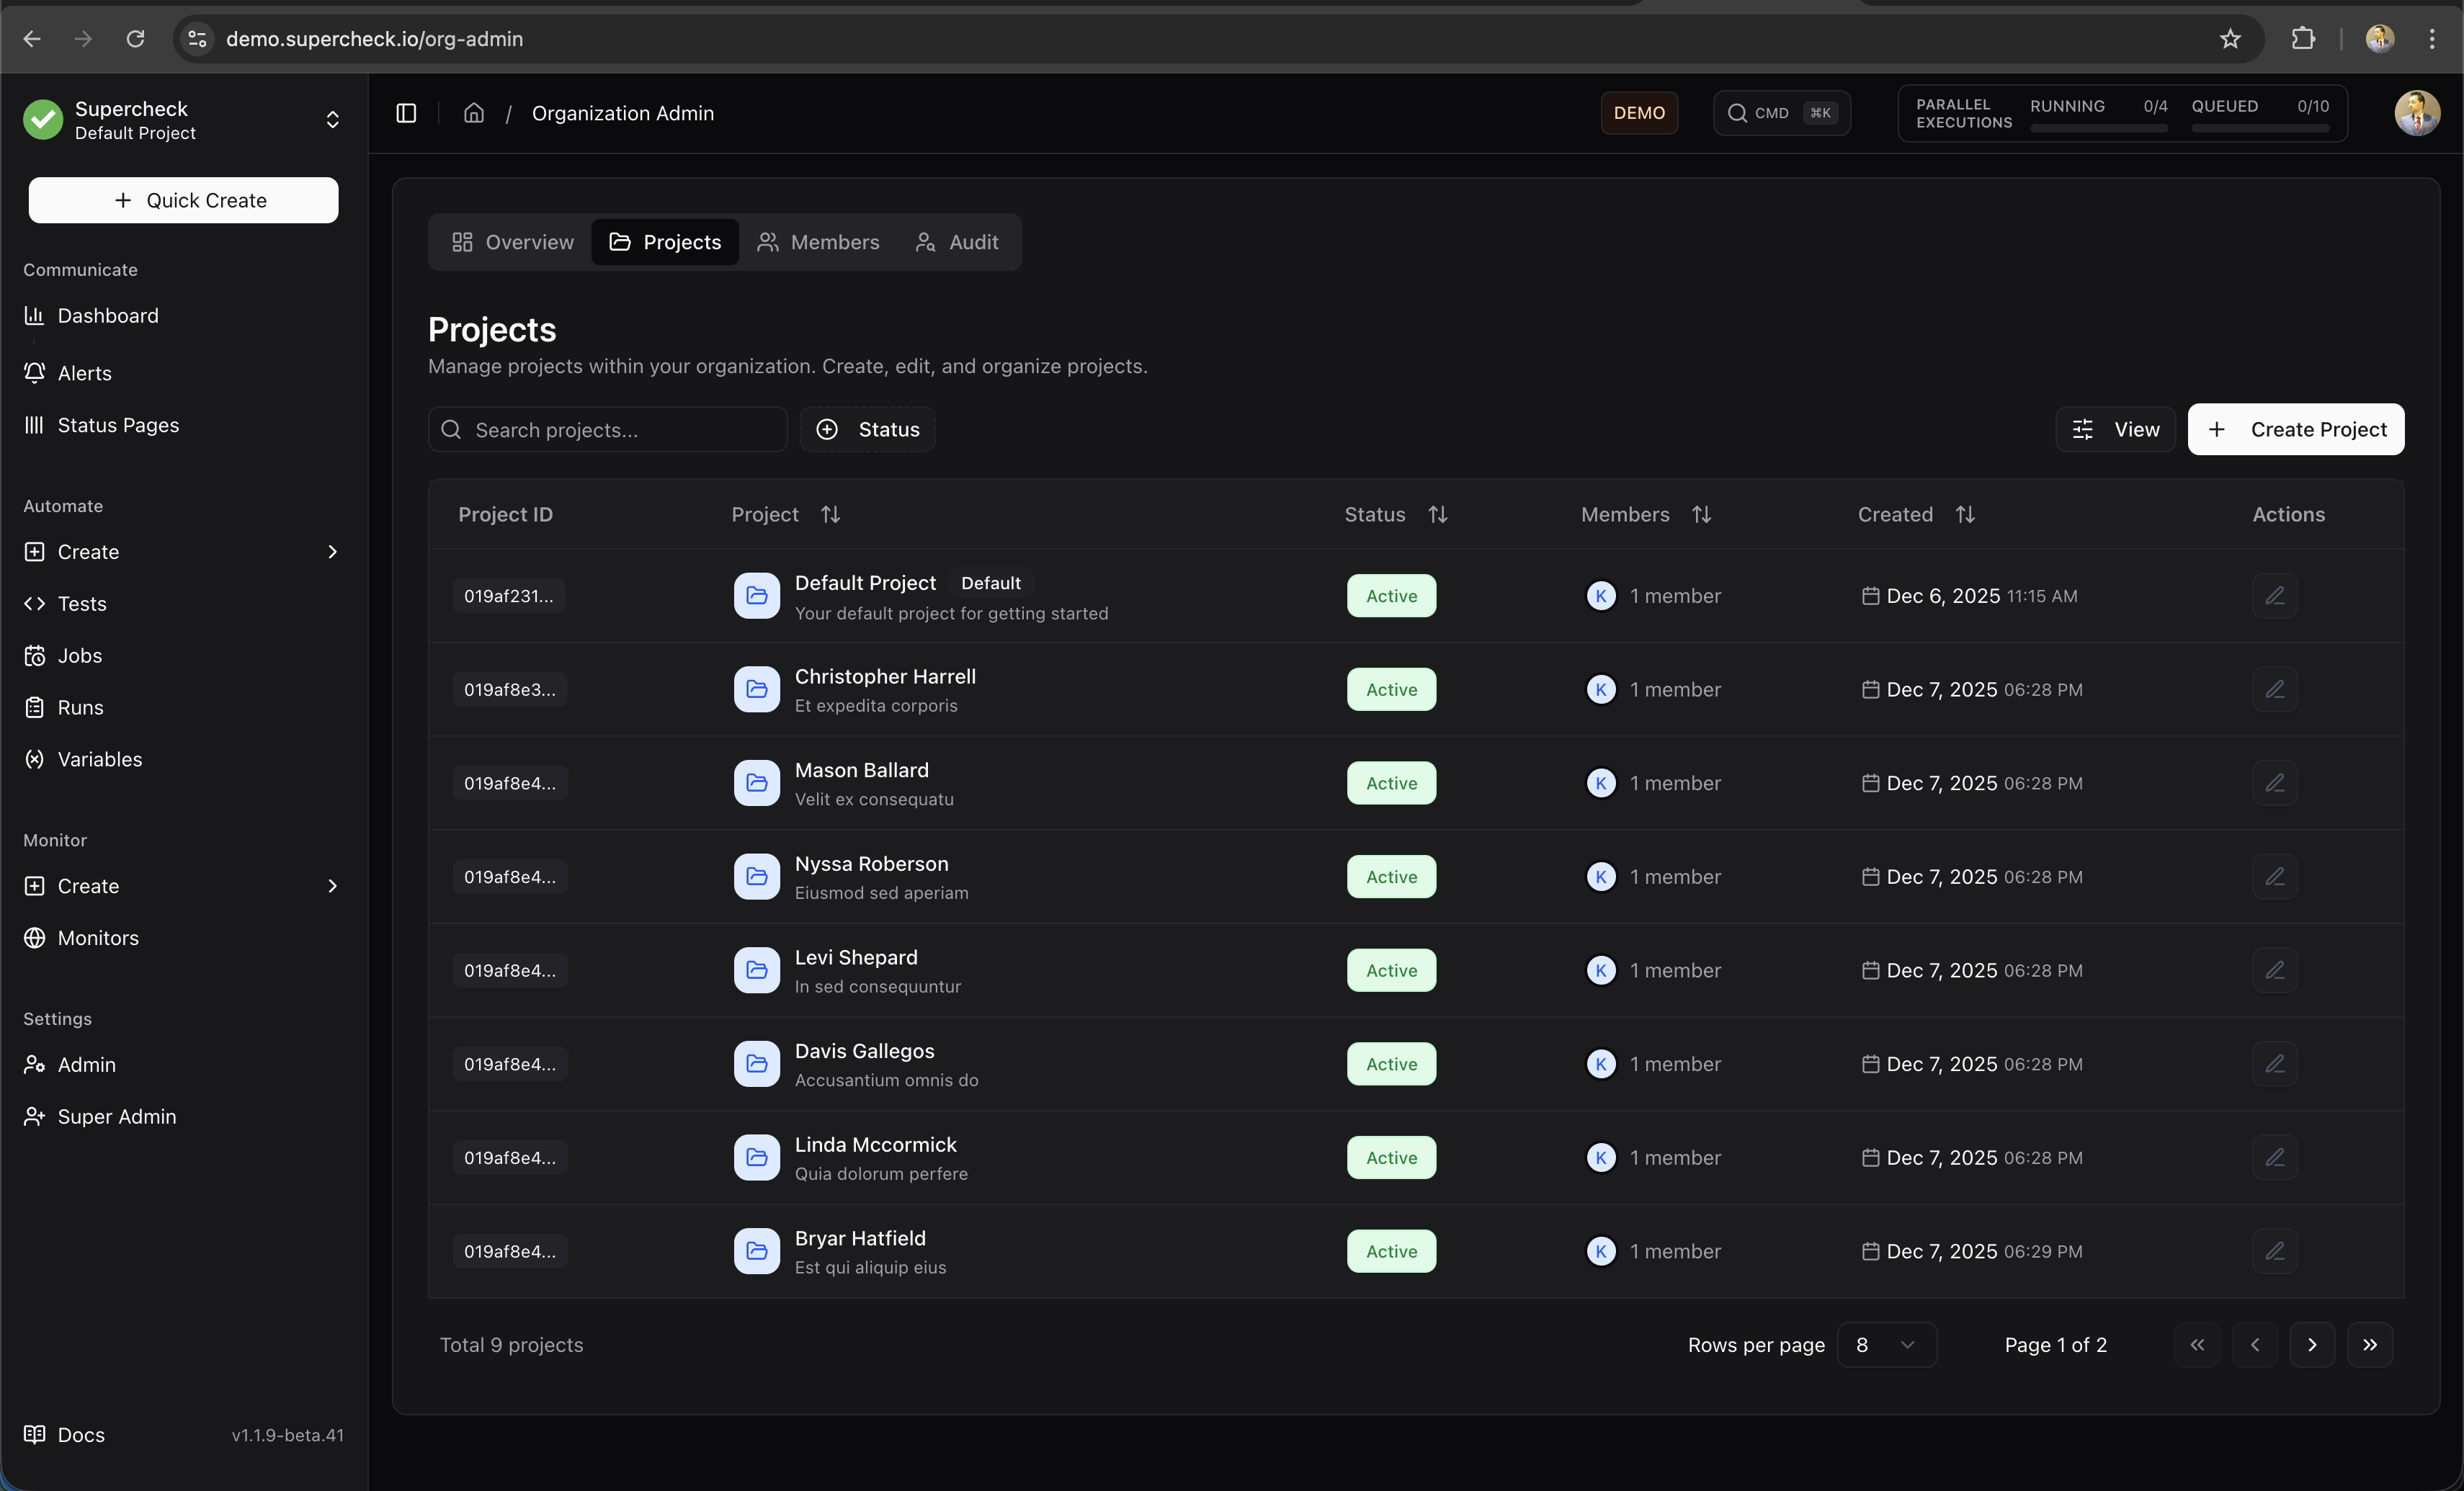
Create Project
Create a new project to organize your tests, jobs, and monitors.
- Go to Admin → Projects
- Click Create Project
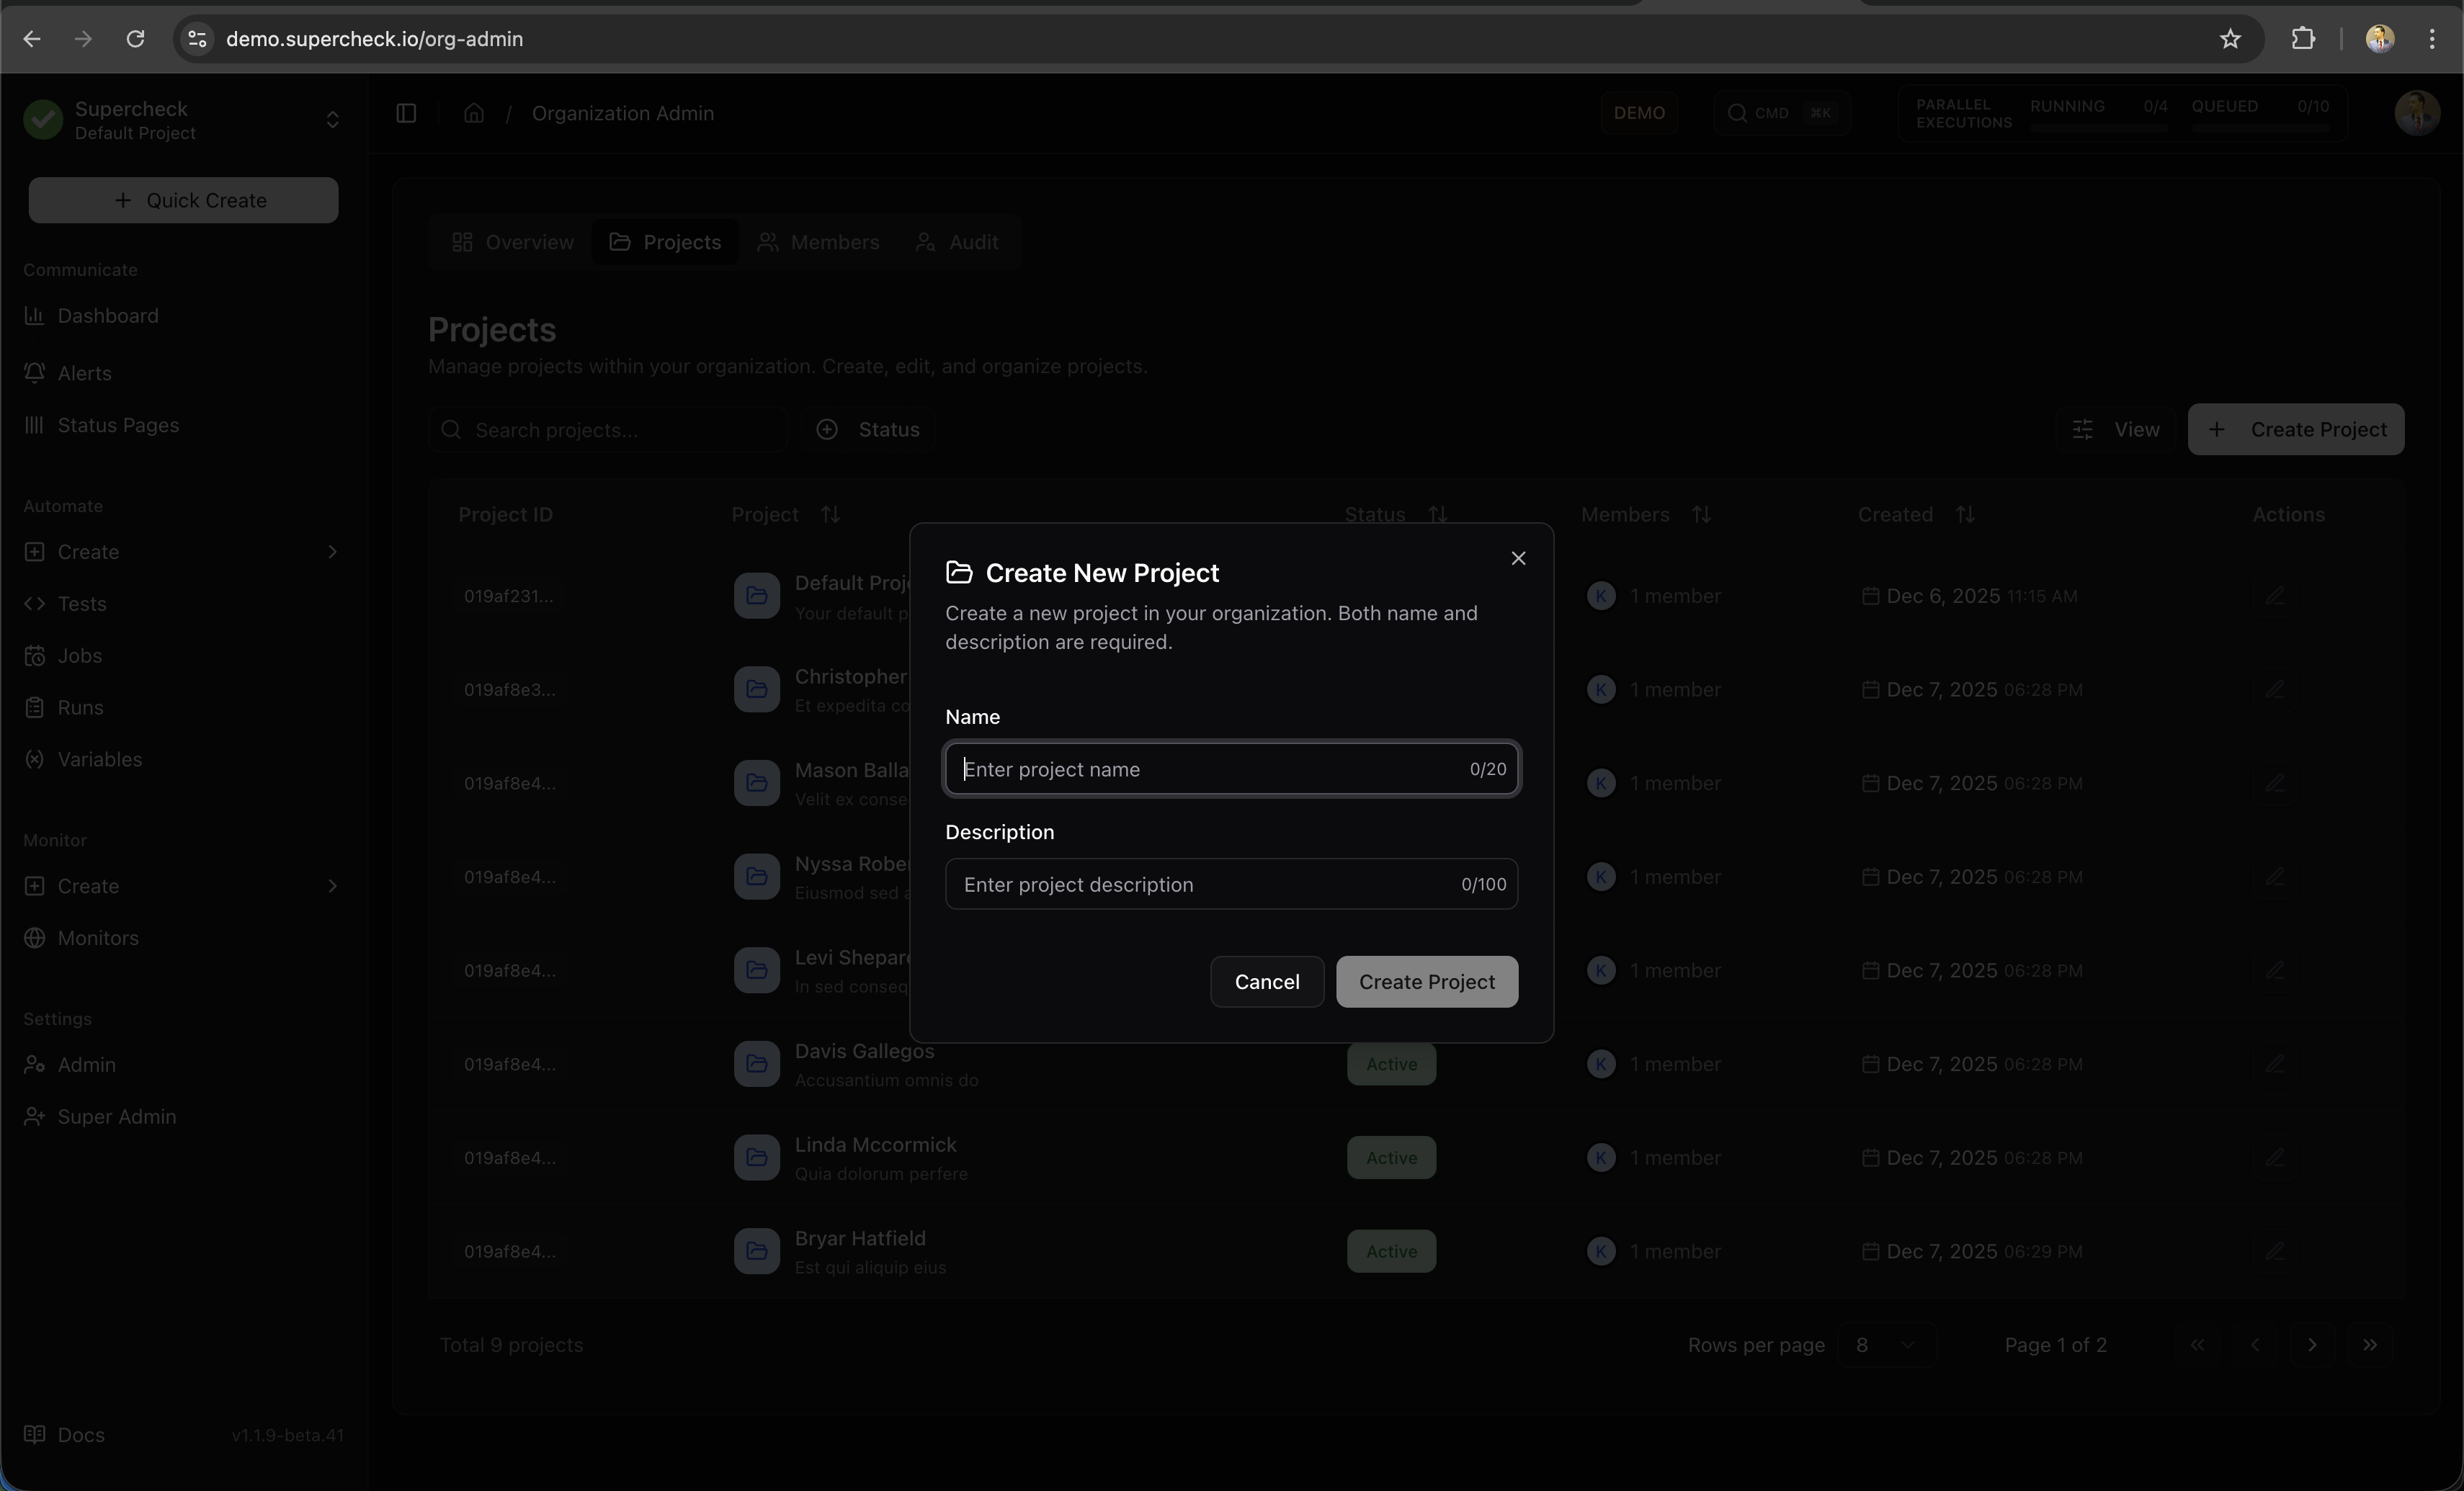
- Enter project name and description
- Configure project settings
- Save
Members
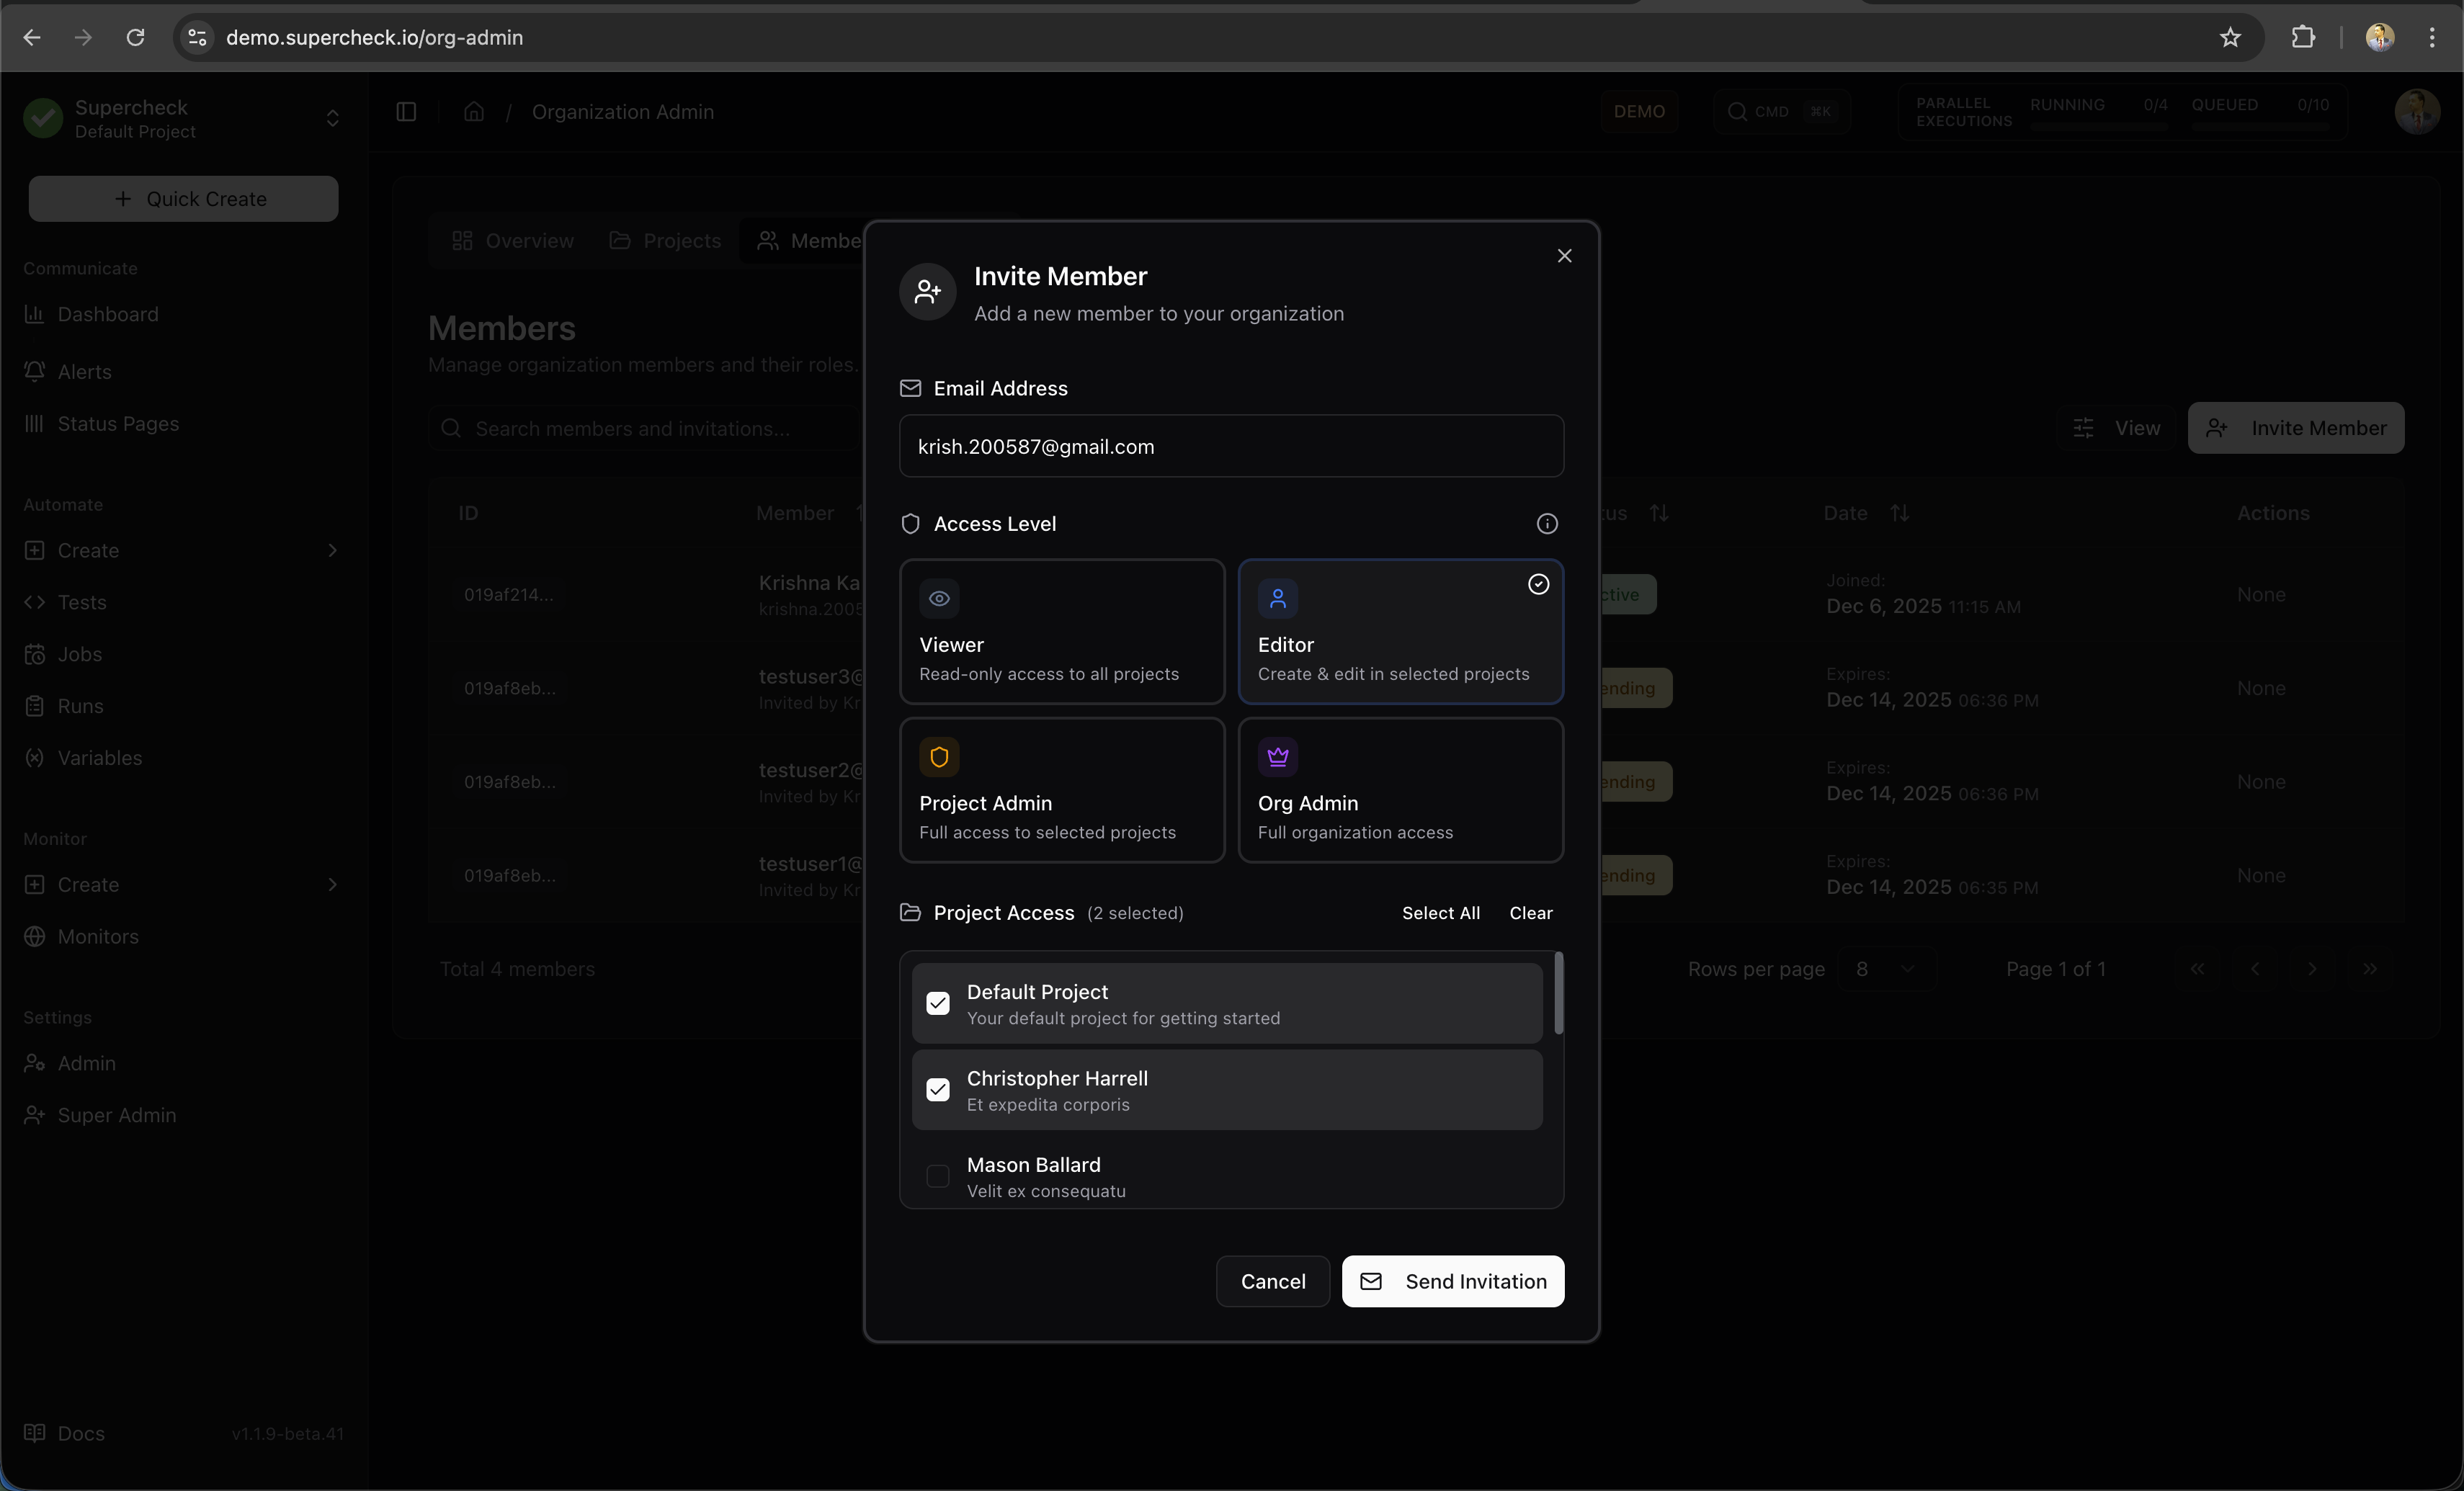
Invite and manage team members with role-based access control.
- Go to Admin → Members
- Click Invite Member
- Enter email and select role
- Send invitation
Roles
The system uses a 6-role RBAC system with specialized roles for organization and project management.
| Role | Permissions |
|---|---|
| Super Admin | System-wide control, user management, and full access to everything. |
| Org Owner | Full organization control, including deletion and member management. |
| Org Admin | Managing members and organization settings (cannot delete org). |
Delete an organization
Only the organization owner can request deletion. Organizations with projects or protected dependencies cannot be deleted through the organization API. Contact your administrator or support to review and remove related data safely.
CLI Tokens
Create project-scoped CLI tokens for API access and automation. Tokens inherit their owner's permissions; use a separate token for each pipeline or integration.
- Go to Admin → CLI Tokens
- Click Create Token
- Enter a name and optional expiry date for a token in the current project
- Copy the generated token securely
AI SRE Setup
Administrators configure project-level AI SRE setup from Admin so responders do not need to manage setup screens during an incident.
The setup tabs are:
- Services — Open the top-level Services page to register production services and ownership metadata used to map alerts, incidents, and connector evidence.
- Integrations — Configure read-only evidence connectors, link alert notification providers to connector context, and optionally save repeatable read-only queries.
- Private Agents — Register and deploy an agent to use private evidence sources in investigations.
See AI SRE setup for the full setup flow.
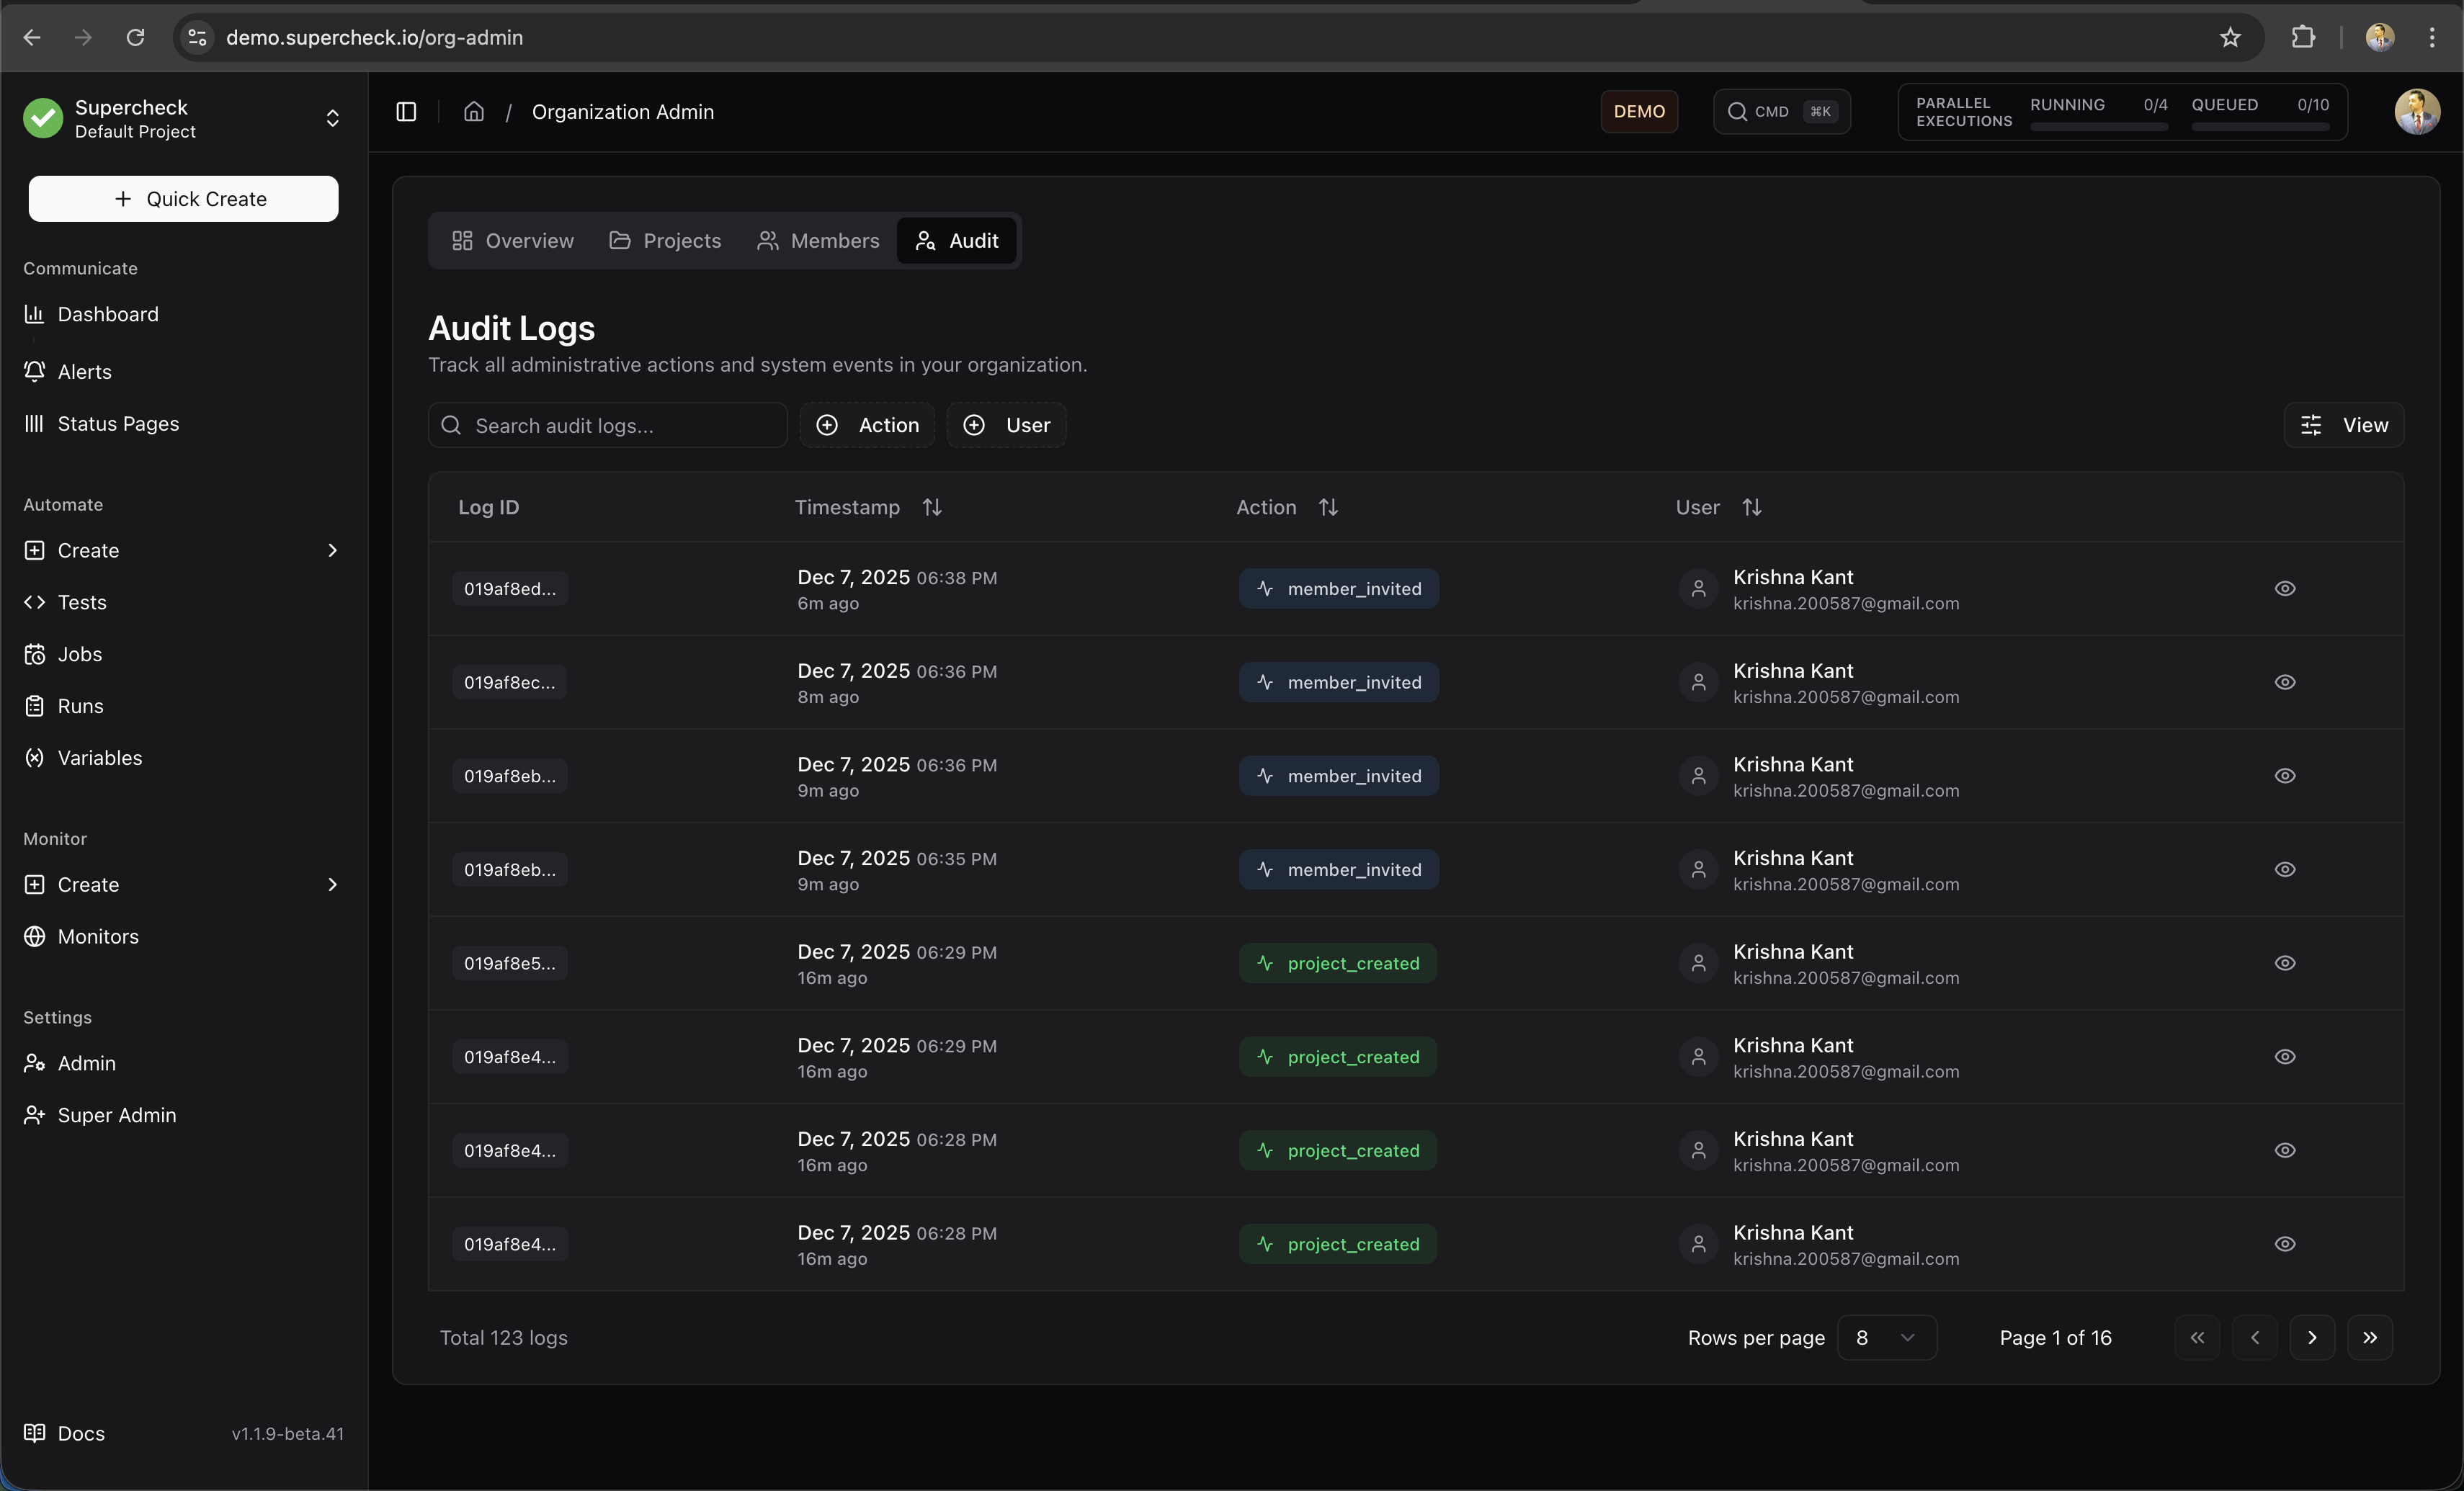
Audit Log
Track all actions performed within your organization. View who did what and when for compliance and security monitoring.
Event Categories
The audit log captures events across these categories:
| Category | Examples |
|---|---|
| Authentication | Login, logout, password resets |
| Authorization | Role changes, permission grants |
| Resource Management | Test creation, monitor updates, job deletions |
| Execution | Manual test runs, job triggers |
| Configuration | Settings changes, integration updates |
| Security | Failed logins, unauthorized access attempts |