
Connectors
Add read-only evidence sources for AI SRE investigationsEdit
Add a connector when an investigation should use evidence from a tool your team already operates. Configure connectors under Settings → Organization → Integrations with a role that can configure connectors.
A connector gives access to a provider. Saved queries are optional reusable questions that run through one enabled connector. You can search a connector during an investigation without saving a query first.
Supported Providers
Choose one of these in Add connector.
| Category | Providers |
|---|---|
| Metrics and dashboards | PrometheusGrafanaAWS CloudWatchGoogle Cloud MonitoringAzure Monitor |
| Operational events | Datadog |
| Logs and search | LokiElasticsearchOpenSearchGoogle Cloud LoggingAzure Log Analytics |
| Distributed traces | Grafana TempoJaeger |
| Application performance (NRQL) | New Relic |
| Cloud and orchestration | Kubernetes |
| Error tracking | Sentry |
| Code and deployments | GitHubGitLab |
| Incident management | PagerDutyOpsgenie |
| Tickets and knowledge | JiraConfluenceNotion |
| Custom tools | MCP servers in your network (Private Agent only) |
For OpenTelemetry, connect the backend your collector exports to (Tempo, Jaeger, Loki, Prometheus, and so on). Slack, Teams and webhooks are notification channels, not connectors.
Choose How to Connect
| Your provider | Choose | What to do |
|---|---|---|
| A public API Supercheck can reach | Direct | Enter the endpoint and read-only credentials. Cloud endpoints must use HTTPS |
| An API reachable only inside your network | Private Agent | Set up an agent with Docker Compose, then select it when adding the connector |
| An internal API reachable from your self-hosted instance | Direct or Private Agent | Use Direct if your instance can reach it. Otherwise deploy an agent in that network |
Private Agent mode supports GitHub, Kubernetes, Prometheus, Grafana, Sentry, Datadog, Loki, Elasticsearch / OpenSearch, Tempo, AWS CloudWatch, Jaeger, New Relic, Splunk, Google Cloud, Azure Monitor, Jira, Confluence, and MCP servers. GitLab, PagerDuty, Opsgenie, and Notion support Direct only.
Add a Connector
Add the connector
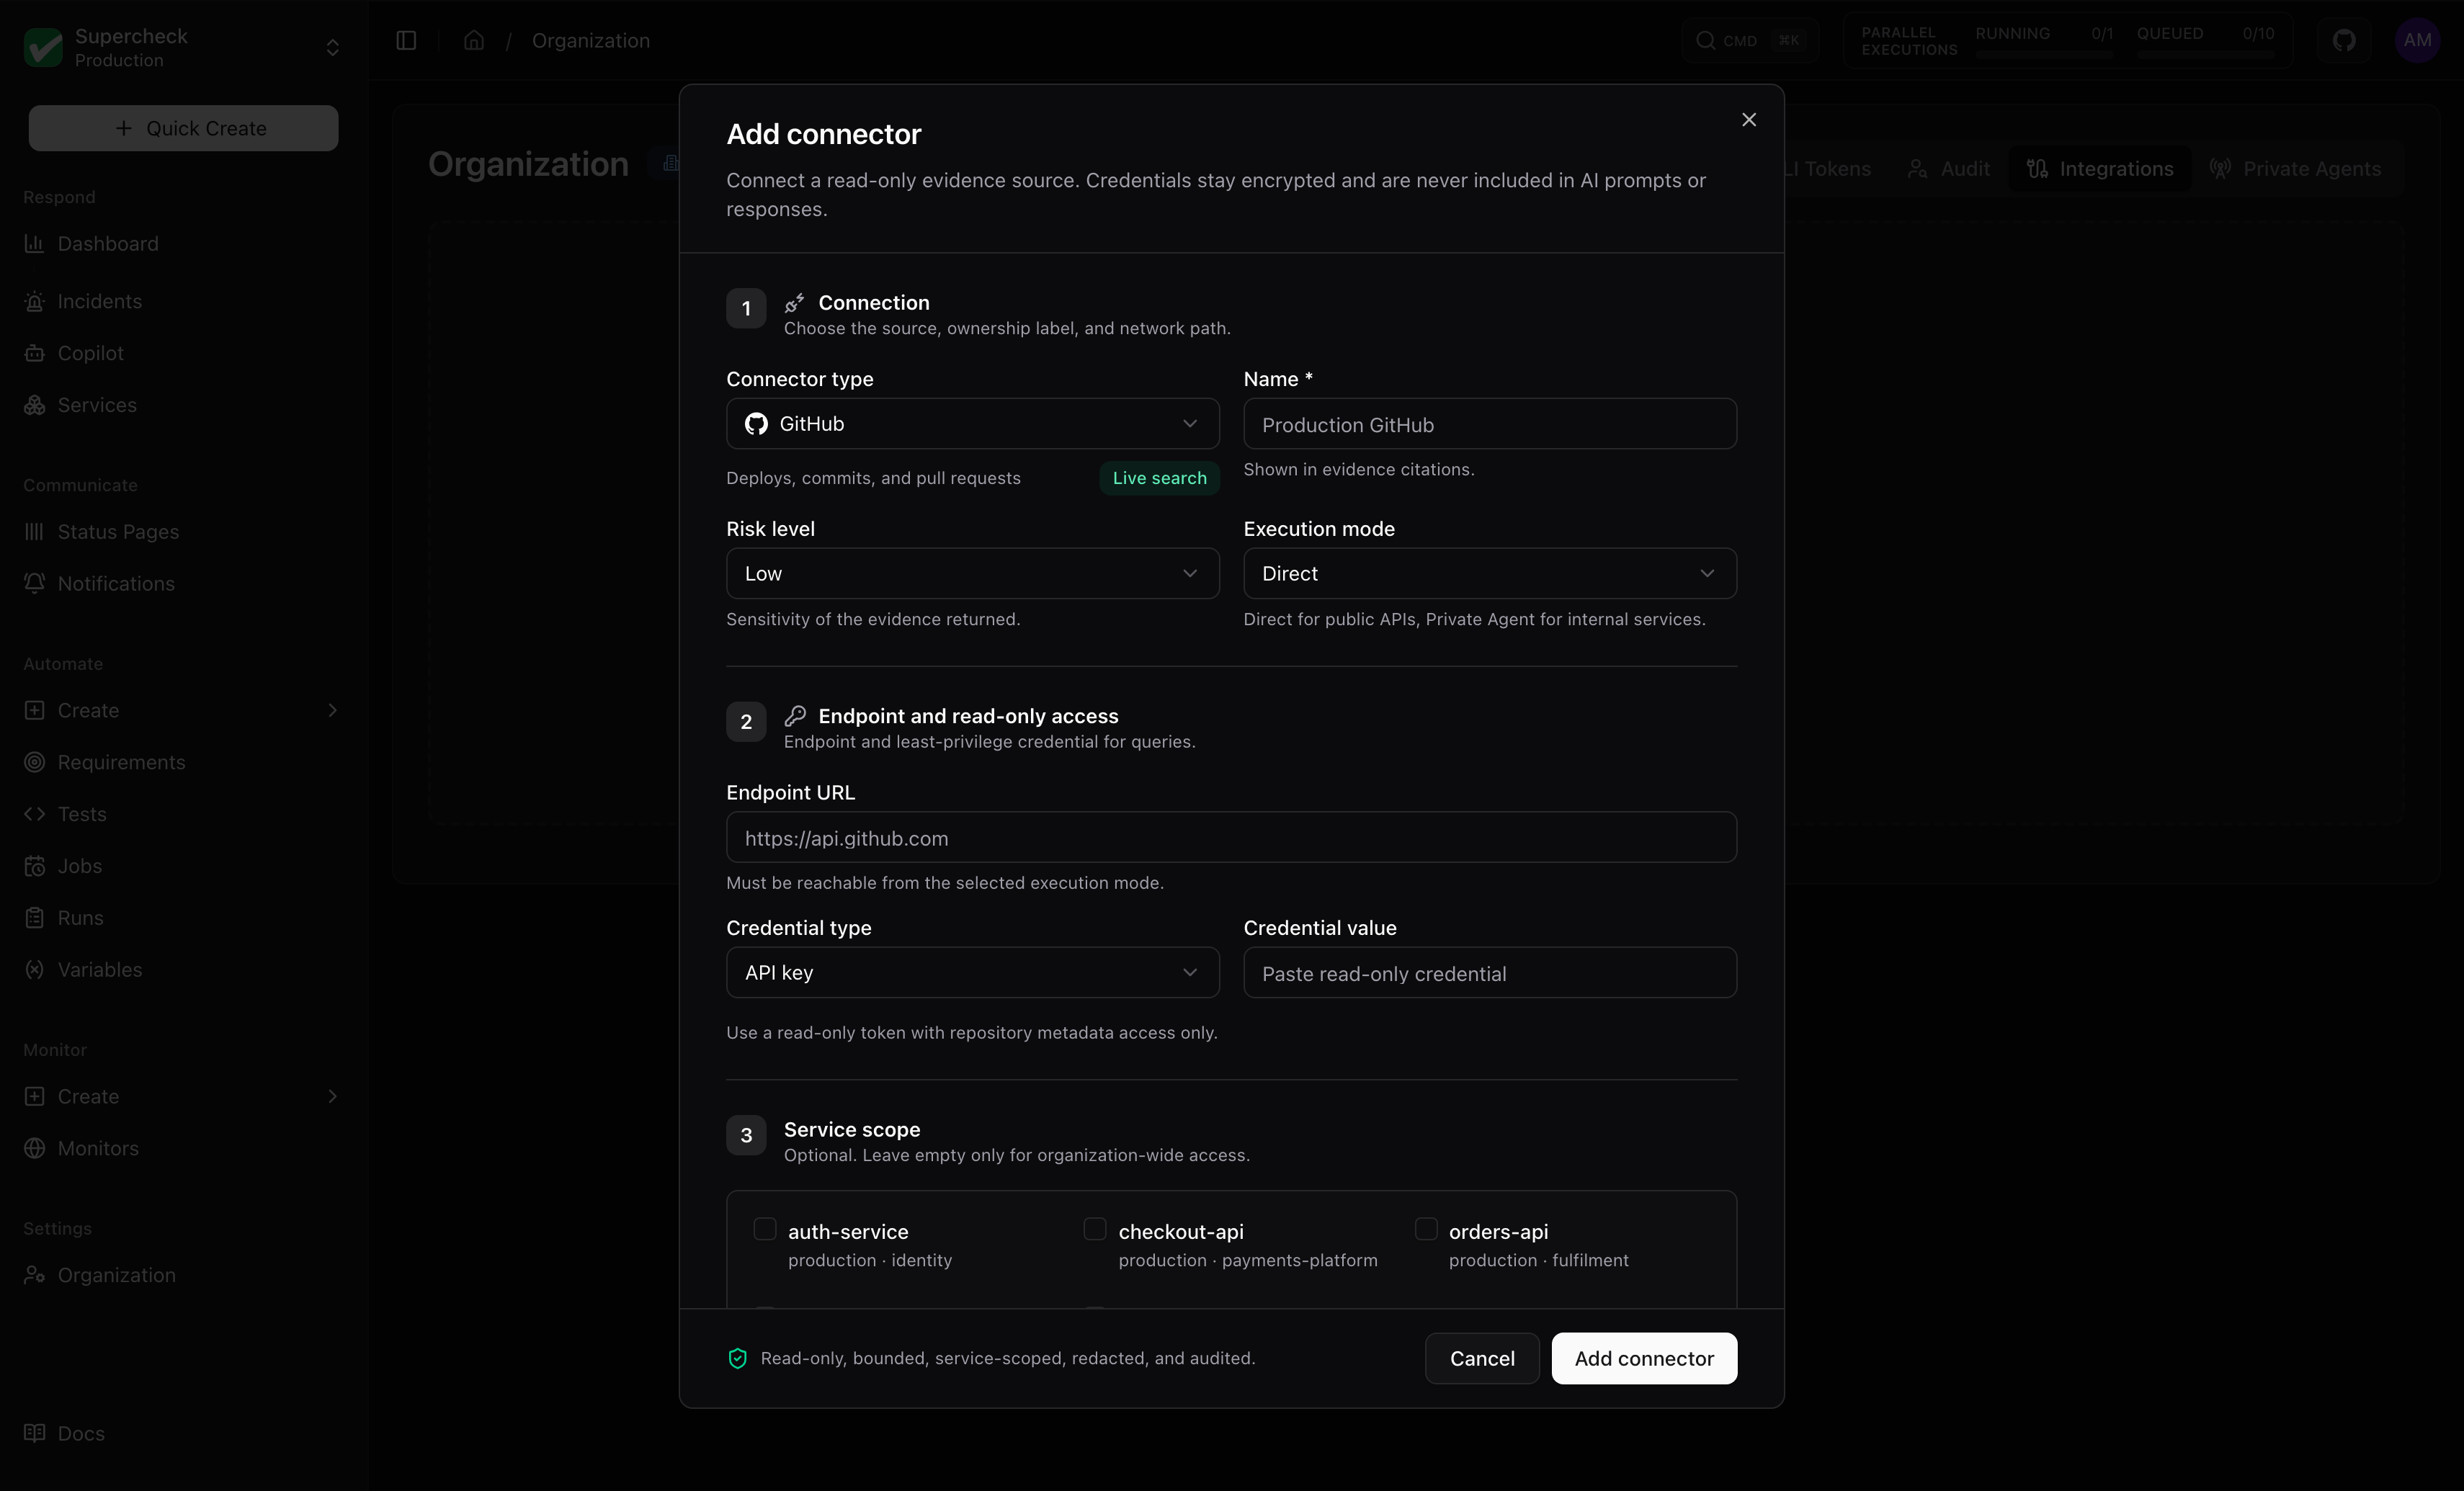
Go to Settings → Organization → Integrations, select Add connector, pick the provider and give it a recognizable name, such as Production GitHub.
Choose the mode
Choose Direct or Private Agent. For Private Agent, first register an agent under Settings → Organization → Private Agents, then select it in the dialog.
Add endpoint, credential and scope
Enter the API endpoint URL and a least-privilege read-only credential, then set the Service scope to restrict which services may use the connector.
Validate
Save, validate, then run one known-result query and one no-result query before relying on the connector during an incident. A host that does not resolve, a refused connection, and a 404 on the endpoint path each get a specific message. A Private Agent connector cannot be probed from Supercheck, so validation shows guidance instead of an error.
Use the smallest service scope and query time window that answer your question. If a search returns no evidence, check the service scope, provider permissions, and time range.
MCP Servers (Private Agent only)
Connect any Model Context Protocol server running inside your network as a read-only evidence source. Supercheck reaches it only through a Private Agent, so Execution mode must be Private Agent. Direct mode is rejected. Only the Streamable HTTP transport is supported. Supercheck never starts local processes or stdio servers.
Add a connector of type MCP with the server's endpoint URL, for example https://mcp.internal.example.com/mcp, and the Private Agent that can reach it. An optional credential is sent as Authorization: Bearer <value>, or as a custom header if you set a header name.
Open Manage MCP tools from the connector menu and select Discover tools. The Private Agent lists the server's tools and their input schemas.
Tick the tools investigations may call and save. Nothing is callable until you allowlist it. You can fix some arguments, such as a namespace, to a constant value that the AI cannot override.
Allowlist only tools that cannot change anything. Supercheck cannot verify what a tool does on your server. Prefer a server or token that exposes read-only tools, and review each tool before ticking it.